
IT professionals carry the core responsibility for every data disposal decision their organization makes. That means more than just wiping drives. It covers selecting the right sanitization method for each media type, maintaining an accurate asset inventory, coordinating with legal and compliance teams, managing compliant vendors, and producing documentation that holds up under a regulatory audit. 2, HIPAA, CCPA, GDPR, and ISO 27001. Each imposes specific obligations on how data is destroyed and how that destruction is proven.
Here is what IT’s core responsibilities look like in practice:
- Asset inventory and classification: Maintain a current register of all data-bearing assets, tagged by data sensitivity and regulatory category.
- Sanitization method selection: Choose clearing, purging, or destruction based on media type, data classification, and applicable standards.
- Approval and oversight: Own the formal sign-off process before any asset leaves the organization’s control.
- Vendor management: Vet, contract with, and audit compliant third-party destruction providers.
- Cross-functional collaboration: Work directly with legal, compliance, and privacy teams to keep disposal practices aligned with current regulations.
- Training: Run awareness programs so every staff member handling end-of-life assets understands the protocols.
Getting any one of these wrong creates liability. Getting all of them right is what defensible data disposal actually looks like.
Table of Contents
- How IT decides which sanitization method to use
- What regulations actually require from IT in data disposal
- Building a data disposal policy that actually holds up
- How to evaluate and manage documented data destruction vendors
- Recycle for Life handles documented data destruction so your team doesn’t have to
How IT decides which sanitization method to use
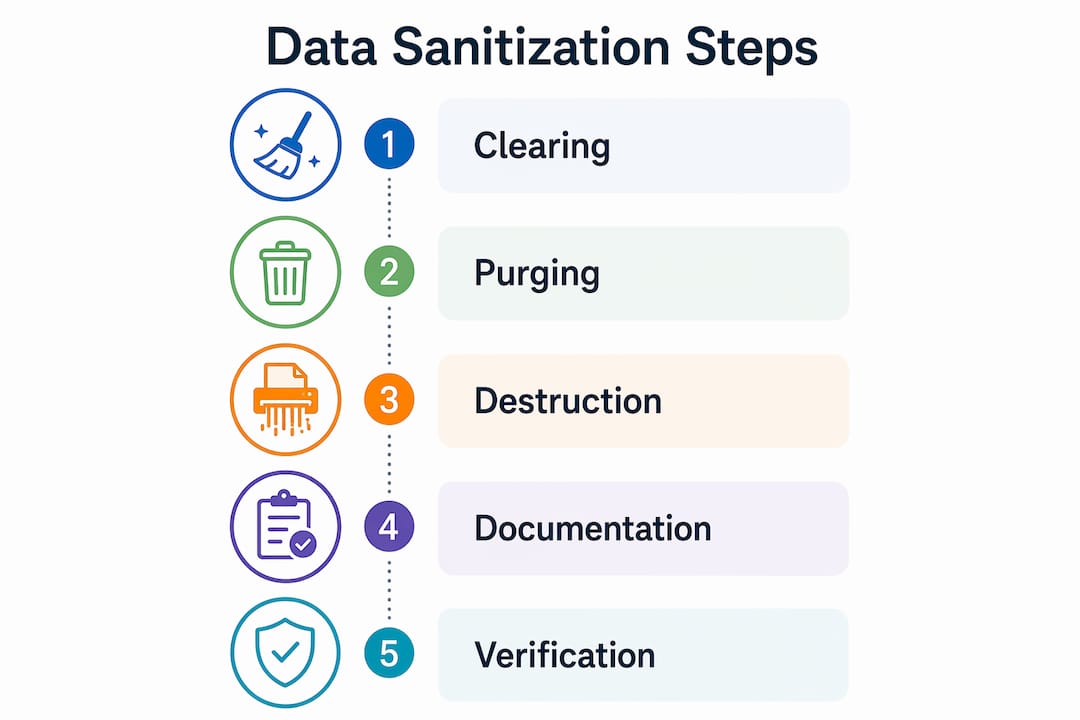
2 organizes sanitization into three tiers: clearing, purging, and destruction. Choosing among them is not arbitrary. The decision depends on storage technology, data sensitivity, whether the asset will be reused, and what tools are operationally available.
Clearing overwrites data using standard read/write commands. It works for magnetic hard drives being repurposed internally, where the risk of recovery is low and the asset stays within the organization. Destruction is physical: destruction, disintegration, or incineration. It is the only fully reliable option for assets leaving the organization permanently or containing data classified at the highest sensitivity levels.
SSDs deserve special attention. Standard OS deletion and quick formats do not remove sensitive data stored in hidden areas and caches; residual data persists in unallocated storage blocks that overwrite commands often miss entirely.
| Sanitization Method | Media Type | Recommended Use |
|---|---|---|
| Clearing (overwrite) | Magnetic HDD | Internal reuse, low-sensitivity data |
| Physical destruction | HDD, SSD, tape, optical | Highest sensitivity, permanent retirement |
| Disintegration | SSD, flash media | Classified or regulated data, no reuse |
Operational considerations IT must account for before choosing a method:
- Volume: High-volume disposal favors automated overwrite tools or contracted destruction services over manual processes.
- Environmental impact: Reuse and resale extend asset life and reduce e-waste. Physical destruction should be reserved for cases where reuse is genuinely not viable, not used as a default because it is easier to document.
- Regulatory floor: Some frameworks set a minimum method. HIPAA-covered entities, for example, cannot rely on clearing alone for protected health information on drives leaving the organization.
IT asset lifecycle management decisions made at procurement, years before disposal, shape how complex and costly sanitization becomes.
What regulations actually require from IT in data disposal
The regulatory picture for U.S. organizations is layered. Federal sector-specific laws, state privacy statutes, and international standards all apply depending on the data types an organization handles and where its customers or employees are located.
HIPAA requires covered entities and business associates to render protected health information unreadable, indecipherable, and otherwise unable to be reconstructed. The HHS guidance specifies clearing, purging, or destruction as acceptable methods. Failure to properly dispose of PHI is a reportable breach, with penalties scaling from $100 to $50,000 per violation depending on culpability.
CCPA (and its amendment, CPRA) requires that California residents’ personal information be destroyed when no longer needed for its original purpose. Organizations must be able to demonstrate that destruction occurred, which means documentation is not optional.
GDPR applies to any U.S. organization processing personal data of EU residents. Under Article 5, personal data must not be kept longer than necessary, and Article 17 creates a right to erasure. ISO 27001 and GDPR both emphasize that organizations must prove data is unrecoverable at asset end-of-life, with documented ownership and verified vendor controls carrying more weight than the destruction method alone.
ISO 27001 is not a law, but it is the international standard most enterprise clients and partners expect. Annex A control A.8.10 specifically addresses media disposal, requiring that storage media containing sensitive information be verified as destroyed or sanitized before disposal or reuse.
Key compliance obligations IT must track:
- Documentation retention: Most frameworks require disposal records to be kept for a defined period. HIPAA audit documentation, for example, must be retained for six years.
- Certificates of Destruction: A missing or inadequate Certificate of Destruction is a major compliance vulnerability; legal responsibility does not transfer until documented proof of destruction is in hand.
- Breach notification triggers: Improper disposal that results in unauthorized access to personal data triggers notification obligations under HIPAA, CCPA, and most state breach notification laws.
- Vendor due diligence: Regulations do not absolve organizations of liability when a third-party vendor mishandles disposal. IT must verify vendor registrations and retain those records.
- State laws beyond CCPA: New York’s SHIELD Act, Virginia’s CDPA, and similar state statutes impose their own disposal requirements. IT must track which state laws apply based on where data subjects are located.
The compliance requirements for data disposal are not static. Regulations evolve, and IT’s role includes monitoring those changes and updating disposal procedures accordingly.
Building a data disposal policy that actually holds up
A data disposal policy is only as strong as its specificity. Generic statements about “securely disposing of data” do not satisfy auditors or regulators. The policy needs to name methods, assign ownership, set timelines, and define what documentation proves completion.
Core policy elements
Asset inventory and classification is the foundation. Every data-bearing asset must be cataloged with its data classification level before disposal decisions can be made. Classification drives method selection, and method selection drives documentation requirements.
Sanitization protocols should be written as decision trees, not general guidelines. If it is a magnetic drive being reused internally, clearing with a verified overwrite tool is acceptable. The policy removes ambiguity so individual technicians are not making judgment calls on the floor.
That includes internal transfers, staging area logs, the Certificate of Recycling issued after pickup, and any Certificate of Destruction.
IT should not be selecting vendors based on price alone.
Roles and responsibilities need to be explicit. Who approves disposal? Who executes sanitization? Who reviews vendor documentation? Who signs off on the final audit trail? Ambiguity here is where disposal gaps emerge, particularly in distributed environments where domain teams assume central IT is handling it.
Best practices for policy components:
- Tie the policy to the asset lifecycle so disposal planning begins at procurement, not at retirement.
- Schedule annual policy reviews aligned with regulatory updates.
- Require IT sign-off before any asset is transferred to a vendor or physically removed from the facility.
- Build in escalation paths for edge cases: damaged drives, legacy media, assets with unclear data classification.
- Integrate disposal records into the broader IT asset management system so nothing falls through the cracks.
Training and awareness programs are a policy element that IT often underinvests in. Staff who handle end-of-life assets, including help desk technicians, warehouse staff, and procurement teams, need to understand why the protocols exist and what the consequences of shortcuts are. Training records themselves become part of the defensible governance documentation that regulators and auditors look for.
Collaboration with legal and compliance teams is not a one-time policy review. IT should have a standing process for flagging regulatory changes, reviewing incident reports involving disposal failures, and updating procedures when the organization’s data footprint changes, such as after an acquisition or a new product launch that creates new data categories.
Pro Tip: Map each policy requirement back to the specific regulation or standard that drives it. When an auditor asks why you destroy SSDs rather than overwrite them, “because our policy says so” is a weak answer.
How to evaluate and manage documented data destruction vendors
Third-party vendors handle a significant portion of enterprise data disposal, which means IT’s vendor management function is a direct extension of its security posture. The wrong vendor does not just create operational problems. It creates regulatory liability that stays with your organization regardless of what the contract says.
Registrations that matter
When choosing a recycler, confirm it is EPA-registered and regulated by the state (in California, the DTSC), with annual reporting on how waste is handled.
ISO 27001 registration from a vendor signals that their information security management system has been independently audited. It is particularly relevant when the vendor handles data in transit between your facility and their destruction site.
Vendor evaluation checklist
- Verify registrations directly with the issuing body, not just from the vendor’s marketing materials.
- Review the vendor’s Certificate of Destruction format before signing a contract. It should include the quantity and description of what was destroyed, the method, the date, and a signature, with serial numbers listed when you supply them.
- Confirm the vendor carries adequate liability insurance and that your contract specifies their liability for a data breach resulting from improper disposal.
- Ask for references from clients in your industry, particularly if you handle regulated data categories like PHI or financial records.
- Audit the vendor periodically. The right to audit should be written into the contract, not just assumed.
On-site destruction, where the vendor brings destruction equipment to your facility, eliminates the transfer risk entirely. For assets containing the most sensitive data, this is worth the additional cost.
The IT disposal documentation process does not end when the vendor picks up the assets. IT must receive, review, and file the Certificate of Destruction, match it against the asset inventory, and flag any discrepancies before closing the disposal record. That final reconciliation step is where many organizations fall short, and it is exactly what auditors check first.
Recycle for Life handles documented data destruction so your team doesn’t have to
When your organization needs secure, documented data destruction without building an in-house destruction operation, Recycle for Life provides a direct path. The service covers hard drive destruction, e-waste recycling, and IT asset recovery with on-site destruction options and official Certificates of Destruction that satisfy HIPAA, CCPA, and ISO 27001 audit requirements.

What sets Recycle for Life apart for IT teams managing compliance-driven disposal is the combination of documented destruction and asset recovery in one workflow. That matters for organizations managing large retirement cycles where disposal costs add up fast.
Recycle for Life offers free quotes and pickup options, which removes the logistical friction that causes disposal backlogs. Backlogs are a compliance risk on their own: assets sitting in a staging area waiting for disposal are assets that can be lost, stolen, or accessed without authorization.
For IT teams that need compliant equipment destruction with full documentation, or organizations looking to handle e-waste recycling with compliance built in, Recycle for Life is the practical next step. Request a quote directly at usedcartridge.com/it-asset-recovery-disposition-quote to get a disposal plan matched to your asset volume and regulatory requirements.
Key Takeaways
IT’s role in data disposal decisions is the organizational control point where technical method selection, regulatory compliance, documentation integrity, and vendor oversight converge into a single accountable function.
| Point | Details |
|---|---|
| Regulations stack, not substitute | HIPAA, CCPA, GDPR, and ISO 27001 can all apply simultaneously; IT must track which frameworks govern each data category and asset type. |
| Policy specificity prevents liability | Disposal policies must name methods, assign ownership, and set timelines; generic language does not satisfy auditors or regulators. |
| Recycle for Life | Provides documented on-site destruction, Certificates of Destruction, and IT asset recovery in one workflow for organizations managing compliance-driven disposal. |