
PCI DSS requires that electronic media holding cardholder data be destroyed or rendered unrecoverable once it is no longer needed, under Requirement 9.4.7. Retention and disposal run on documented policy, with teams verifying at least once every three months that expired data has actually been removed, per Requirement 3.2.1. What follows is a checklist, the evidence auditors ask for, and the vendor controls that make certificates defensible.
TL;DR:
- Regularly verify every three months that data exceeding its documented retention period has been properly deleted or rendered unrecoverable.
- Maintain a detailed inventory of all storage locations, including virtual, physical, and removable media, linked to asset tags and your IT asset management system.
- Require certificates of destruction to include precise asset identifiers, sanitization methods, operator and verifier names, and timestamps for audit traceability.
Table of Contents
- What PCI DSS actually requires for retention and disposal
- Scope and inventory: where PCI data hides
- Sanitization methods and when to use them
- Building the operational checklist from policy to verification
- Records, certificates, and what assessors expect
- Locking down third-party disposition
- How a compliance-minded disposal program actually runs
- Where compliance programs usually fall apart
- How Recycle for Life can help close the evidence gap
- Sources
- FAQ
What PCI DSS actually requires for retention and disposal
Two clauses carry the weight here. Requirement 3.2.1 says you minimize stored account data: document retention periods with a business or legal justification, cover every location where account data lives, and verify quarterly that anything past its retention window has been deleted or rendered unrecoverable, as TrustedSec details. Requirement 9.4.7 covers the physical and electronic endgame: media containing cardholder data gets destroyed, or the data on it gets rendered unrecoverable, once there is no remaining business or legal reason to keep it, per PCI DSS v4.0.1.
Sensitive authentication data is stricter still: it cannot be stored after authorization completes, full stop. Legal holds are the one legitimate exception to a retention schedule, and they need their own documentation trail.
- Document retention periods with a stated business or legal justification for each data type.
- Verify quarterly that data past its retention window has been deleted or rendered unrecoverable.
- Record any legal hold separately, with scope and expected release date.
Scope and inventory: where PCI data hides
A disposal policy is only as good as the inventory behind it. Cardholder data turns up in places compliance teams routinely miss, and missing one is the fastest way to fail an assessment.
- Map every endpoint, server, and virtual disk image where account data could land, including snapshots.
- Reconcile your backup catalog against retention schedules so expired backups are flagged, not forgotten.
- Inventory removable media, printer and scanner hard drives, and any device with local storage, a category covered in more depth in printer hard drive disposal.
- Search support tickets, screenshots, and logs for incidentally captured cardholder data.
- Include paper records: receipts, batch reports, and manually logged transactions.
- Flag equipment under RMA, lease, or vendor-managed backup as high-risk blind spots, since custody and disposal responsibility often blur there.
Tie every item to an asset tag and link it to your CMDB or ITAM system. Without that linkage, an auditor has no way to confirm the inventory is complete.
Sanitization methods and when to use them
2, finalized in September 2025, defines three sanitization outcomes and expects the method chosen to match the media type and data sensitivity rather than a one-size-fits-all process. Clear uses standard read and write commands to overwrite data logically. Destruction physically disfigures the media so it cannot be reused or read.
- Hard disk drives: overwrite or purge for reuse; destroy when the drive is damaged or leaving custody entirely.
- Paper: cross-cut destroy or incinerate.
Pro Tip: Default to physical destruction for any drive leaving your custody, such as an RMA or a decommissioned asset headed to resale, unless you can produce verified key-zeroization evidence for that specific drive.
Building the operational checklist from policy to verification
Treat disposal as a workflow, not a one-time event. Codify the retention schedule, the acceptable sanitization methods per media type, the roles authorized to approve disposal, and how exceptions like legal holds get handled and recorded.
- Draft a disposal policy naming retention periods, approved methods by media type, and approver roles.
- Require every disposal ticket to carry an asset identifier, a flag for whether cardholder data scope applies, retention approval, chosen method, operator name, verifier name, and timestamp.
- Add third-party fields when a vendor is involved: company name, contract reference, and certificate number.
- Run quarterly verification combining automated scans of storage locations with manual sampling of physical media logs.
- Escalate any failed sanitization attempt immediately and hold the asset until resolved.
- Log every legal hold exception with scope and expected release date, separate from the standard disposal log.
At least once every three months, verify that account data stored beyond its documented retention period has been removed, a cadence TrustedSec ties directly to Requirement 3.2.1. Missing that cadence is one of the more common gaps assessors flag. A planning template for rolling this out across a business appears in electronics disposal planning steps.
Records, certificates, and what assessors expect
Assessors do not accept a generic certificate of destruction at face value. 2. The evidence package assessors want includes an asset identifier, the retention justification, an authorization record, the method applied, operator and verifier names, a timestamp, and a certificate reference that ties back to that exact asset.
- Sample certificates against your asset inventory, not just against vendor invoices.
- Require serial numbers or asset tags on every certificate, not a bulk summary count.
Common failures include certificates listing only a batch quantity with no serial numbers, disposal lists that never get reconciled against the asset inventory, and vendor paperwork that describes the service generically rather than the method applied to that specific drive. Each one breaks the link an auditor needs to trace a decommissioned asset to its proof of destruction. More detail on building an auditable record sits in disposal of data.
Locking down third-party disposition
Hand cardholder-bearing media to a vendor and you inherit their process gaps unless the contract says otherwise. The safest default is destruction, not sanitization, for anything leaving your direct custody through an RMA, a lease return, or an offsite transfer, unless the vendor can produce traceable sanitization evidence for that specific asset.
- Require certificates to list asset or serial numbers, not an aggregate count.
- Require sealed, tamper-evident packaging for transport and a receipt confirming unbroken custody.
- Reserve on-site destruction for anything above your risk tolerance for transit exposure.
Sample vendor certificates regularly rather than filing them unread, and treat recycling partners the same way, a point covered in recycling electronic waste properly.
How a compliance-minded disposal program actually runs
Disposal is governance, not a destruction event. It is policy, authorization, execution, and verification, each one producing a record the next one depends on. An assessor examining Requirement 9.4.7 is not looking for a single receipt; they are looking for a chain that holds together from the ticket that authorized disposal to the certificate that proves it happened.
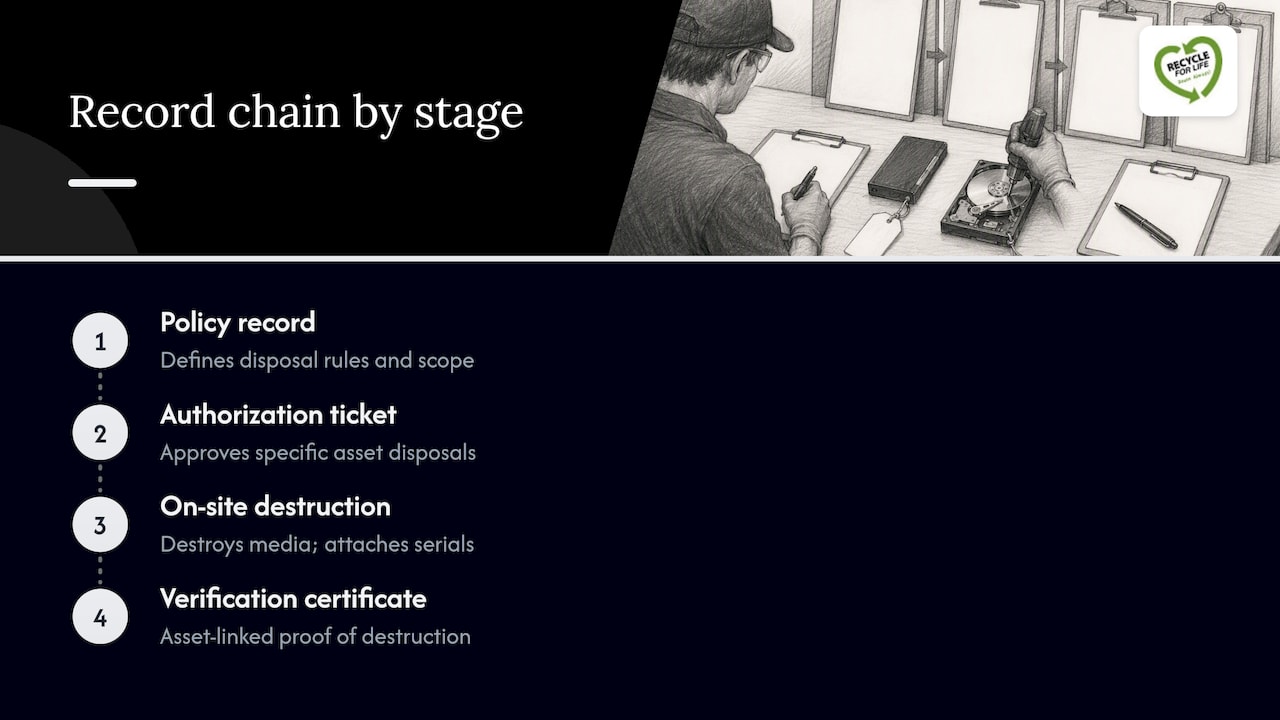
On-site destruction closes the biggest gap in that chain: custody never transfers before the media is destroyed, so there is no transit window to account for.
Where compliance programs usually fall apart
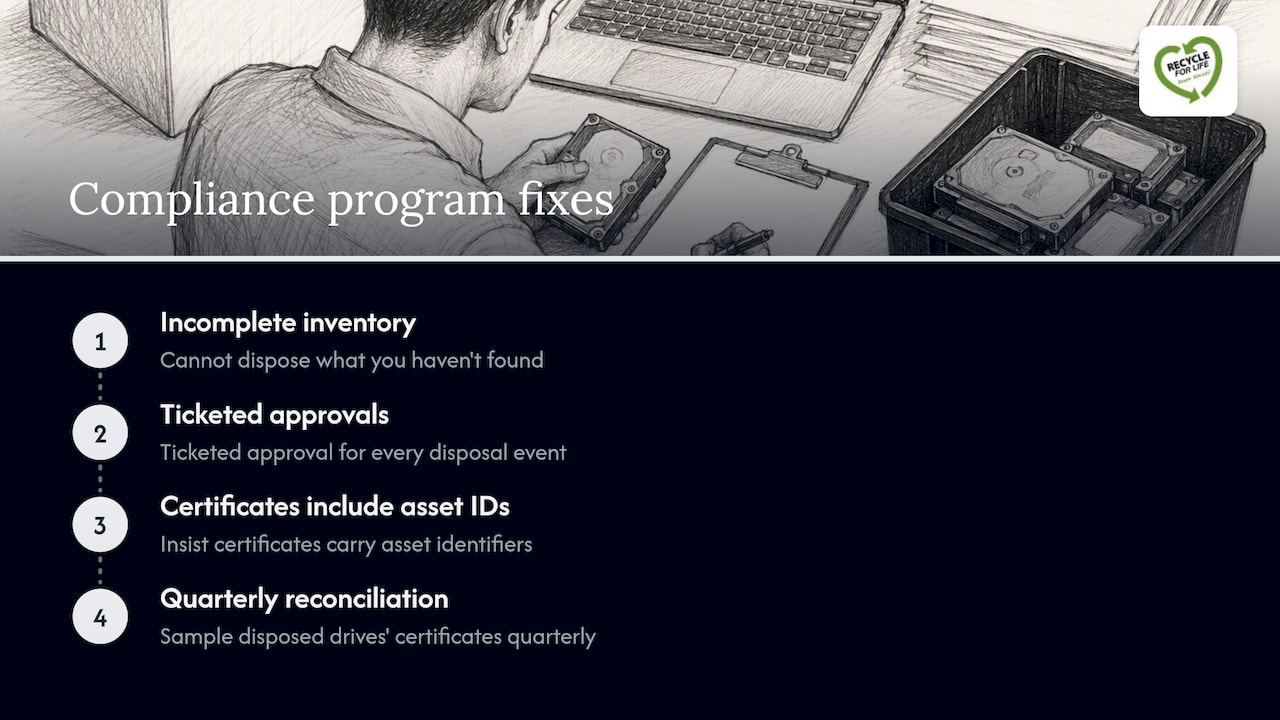
The three failures we see most often are an incomplete inventory, evidence that cannot be traced to a specific asset, and third-party contracts that never spell out what a certificate has to contain. Any one of them can undo an otherwise solid policy.
Fix the inventory first: you cannot dispose of what you have not found. Then enforce ticketed approval for every disposal event, and insist certificates carry asset identifiers you can sample against your own records every quarter. If you do nothing else this quarter, pull your last batch of disposed drives and try to reconcile each certificate to a specific asset ID. The gaps that surfaces will tell you exactly where your program needs work.
How Recycle for Life can help close the evidence gap
Onsite Data Destruction services provide destruction without a custody transfer, which removes the transit question an assessor would otherwise ask about. 
Hard Drive Destruction and IT Asset Disposition/Recovery Services include certificates and pickup, so the record provided to an assessor ties back to the specific assets involved rather than a generic batch count. If your disposal program needs evidence that holds up to sampling, request a quote for onsite data destruction and start building that chain now.
Sources
2 directly. For the PCI requirement text itself, see PCI DSS v4.0.1, and for assessor-facing evidence expectations, the PCI DSS quick reference guide outlines what examiners look for.
FAQ
What counts as PCI data that requires disposal?
PCI data covers cardholder data such as the primary account number, and sensitive authentication data like the full track, CVV, or PIN, wherever it is stored electronically or on paper. Sensitive authentication data cannot be retained after authorization completes, while cardholder data follows your documented retention schedule.
How often must stored account data be verified for deletion?
PCI DSS Requirement 3.2.1 requires verification at least once every three months that account data past its retention period has been deleted or rendered unrecoverable, according to TrustedSec. Most programs pair an automated scan with a manual sample of physical media logs on that cadence.
Is cryptographic erase acceptable for PCI disposal?
2, but only when no plaintext existed before encryption and key zeroization is documented and traceable.
What should a certificate of destruction include?
A usable certificate names the specific asset or serial number, the sanitization method applied, and the date, rather than reporting a bulk quantity for a batch.
What are the PCI requirements for 2026?
PCI DSS v4.0.1 remains the operative standard, and its disposal-related clauses, Requirement 3.2.1 on retention and Requirement 9.4.7 on destroying or rendering media unrecoverable, apply unchanged. Check the PCI Security Standards Council directly for any published updates before an assessment cycle.