
A single improperly disposed hard drive can expose thousands of customer records, trigger regulatory fines reaching $4.4 million under HIPAA, and permanently damage your organization’s reputation. IT managers face mounting pressure from regulations like GDPR, HIPAA, and SOX to prove that decommissioned storage media is truly unrecoverable. Yet many organizations still rely on ad hoc deletion or basic formatting, which leaves data fully retrievable. This guide walks you through the compliant, regulation-aligned steps for hard drive destruction, from understanding compliance standards to executing verified physical destruction, so your team can close every compliance gap with confidence.
Need drives destroyed? See our hard drive destruction service in Orange County, Los Angeles and San Diego: free for 50 or more drives, on-site destruction you can watch on request, and a signed Certificate of Destruction.
Table of Contents
- Understand registration and regulatory standards
- Prepare: Inventory, classify, and plan
- Execute: Documented hard drive destruction methods
- Document, verify, and audit results
- A practical checklist IT pros rarely use — but should
- Get compliant e-waste and data destruction solutions
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| Compliance is critical | Following documented destruction standards protects against data breaches and regulatory risk. |
| Plan before you destroy | Accurate inventory and risk classification ensure the right method and documentation. |
| Choose the right method | Use documented destruction or disintegration with vendor audits for high-security needs. |
| Verify and document all steps | Maintain thorough records and verify destruction for compliance and peace of mind. |
Understand registration and regulatory standards
Documented hard drive destruction is not just about physically breaking a drive. It means following documented, auditable processes that meet recognized standards, so your organization can prove data is unrecoverable to regulators, auditors, and clients.
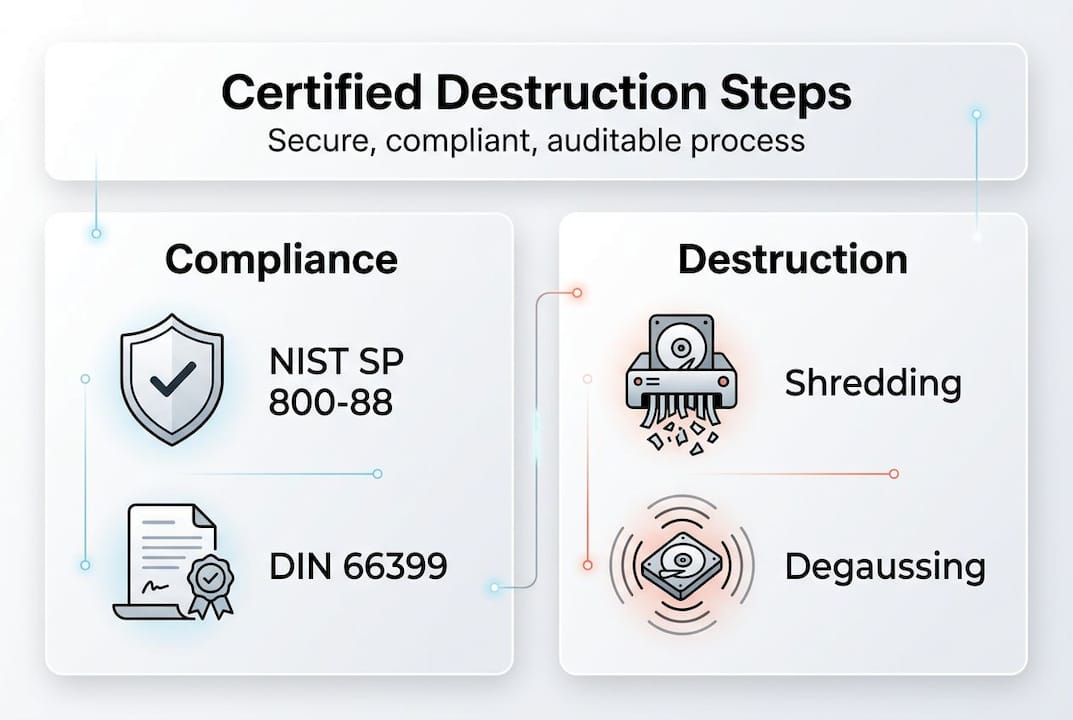
DIN 66399 is a German standard widely adopted across Europe that categorizes media into protection classes and specifies particle sizes for physical destruction.
- Clear: Overwriting data using software tools, effective for low-sensitivity media being reused internally.
- Destroy: Physical destruction through destruction, disintegration, or pulverization, making media completely non-functional.
For most businesses handling regulated data, the Destroy method is the only defensible choice when retiring drives permanently. Review the equipment destruction standards that align with these methods to understand which applies to your hardware.
| Sanitization method | Recovery risk | Best use case |
|---|---|---|
| Clear | Low to moderate | Internal reuse, low-sensitivity data |
| Purge | Very low | Moderate-sensitivity, regulated environments |
| Destroy | None | High-sensitivity, end-of-life media |
Compliance also requires an audit trail. Every destruction event must be documented with a certificate of destruction recording what was destroyed, the method, and the date, with serial numbers listed when you supply your list in advance. Keep your own serial-level inventory alongside it. Without this paper trail, you cannot satisfy a HIPAA audit or a GDPR data subject request.
Understanding e-waste compliance requirements alongside data destruction standards ensures your program covers both environmental and security obligations simultaneously.
Prepare: Inventory, classify, and plan
With standards clearly defined, the next step is building the foundation before a single drive is touched. Skipping preparation is the most common reason organizations end up with compliance gaps.
Start with a complete media inventory. This means cataloging every storage device in your environment, including HDDs, SSDs, USB drives, magnetic tapes, and embedded storage in printers or network equipment. Many IT teams are surprised to discover storage media in devices they never considered, like multifunction printers with internal hard drives.
Once inventoried, classify each asset by sensitivity level. Program setup requires inventory, risk classification, and annual vendor audit as foundational steps in a compliant media sanitization program. Use these four tiers:
- Low risk: Publicly available data, no regulatory obligations.
- Moderate risk: Internal business data, some regulatory exposure.
- High risk: Customer PII (personally identifiable information), financial records, health data.
- Classified: Government or defense contractor data requiring NSA-approved methods.
Map each asset type to its required sanitization method, assign responsible staff, and set timelines for decommissioning. This workflow becomes your repeatable process, not a one-time project.
Pro Tip: Before signing any vendor contract, request their certificate of destruction template, proof of liability insurance, and a sample audit report. A vendor who hesitates to share these documents is a vendor you should not trust with your regulated data.
Vendor due diligence is non-negotiable. Verify that any third-party destruction provider has an EPA ID number, is regulated by the state (the DTSC in California), and issues a Certificate of Destruction. Use e-waste logistics planning resources to understand how compliant vendors structure their pickup and transport protocols.
| Vendor evaluation criteria | What to verify |
|---|---|
| Certificate of destruction | Records what was destroyed, method and date; your serial list attached if supplied |
| Annual audit | Third-party verified compliance |
A well-prepared plan transforms destruction from a reactive task into a controlled, auditable program.
Execute: Documented hard drive destruction methods
Once your plan is ready, execution is where compliance becomes real. Choosing the wrong method for your media type or security level is a costly mistake.
Destruction is the most widely used physical destruction method. For HDDs, documented destruction must produce particles smaller than 6mm. For SSDs, the requirement tightens to less than 2mm because flash memory chips are smaller and can survive larger particle sizes intact.
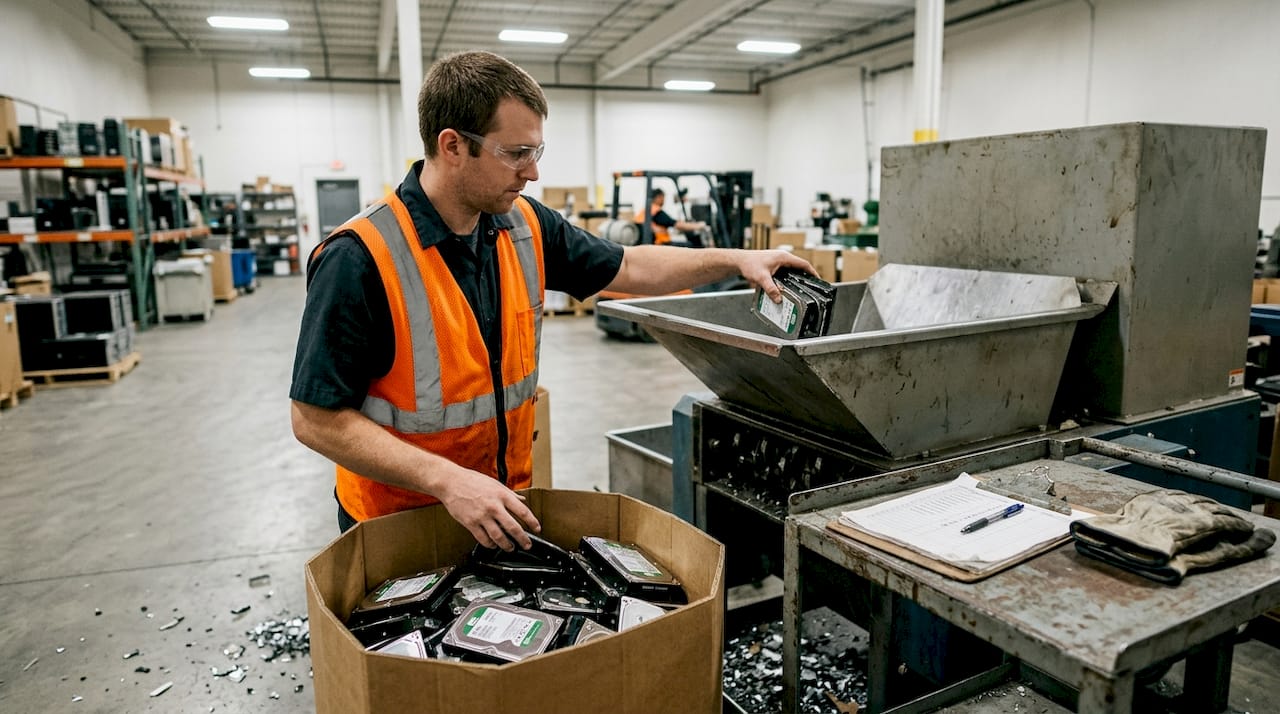
It is fast and effective for HDDs and magnetic tapes, but it does nothing to SSDs, which store data on non-magnetic flash chips. This is a critical distinction many IT teams miss.
Pulverization and disintegration are used for the highest security environments. Pulverizers crush media into fine powder. Disintegrators cut media into particles as small as 0.6mm. These methods are typically reserved for classified government or defense applications.
- Destruction: Best for most commercial and regulated environments.
- Pulverization: Reserved for classified or extremely sensitive environments.
“Applying the wrong sanitization method to the wrong media type is functionally equivalent to not sanitizing at all.”
Review HDD destruction equipment options to understand what compliant devices look like in practice.
Pro Tip: Always request a live demonstration or video evidence of destruction for your first batch with any new vendor. This one step catches non-compliant practices before they become your liability.
Document, verify, and audit results
Physical destruction is only half the job. Without rigorous documentation and verification, your organization cannot prove compliance when it matters most.
Follow these steps for every destruction event:
- Record asset details: Serial numbers, make, model, and data classification level for every drive destroyed.
- Log destruction details: Date, time, method used, technician or vendor name, and location of destruction.
- Issue a certificate of destruction: A signed document from the responsible party confirming destruction was completed per the specified standard.
- Conduct physical inspection: For the Destroy method, verify remnant particle size meets the required threshold, under 6mm for HDDs and under 2mm for SSDs.
- Perform readback verification: For Clear and Purge methods, attempt to read overwritten sectors to confirm data is inaccessible.
Verification steps include readback for Clear and Purge methods, inspecting remnant size for Destroy, and auditing vendors yearly as part of a complete compliance program.
Pro Tip: Store destruction records for a minimum of seven years. HIPAA requires six years, SOX requires seven, and some state privacy laws extend beyond that. When in doubt, keep records longer.
| Regulation | Minimum record retention | Key requirement |
|---|---|---|
| HIPAA | 6 years | Document destruction of PHI media |
| SOX | 7 years | Financial data destruction audit trail |
| GDPR | Duration of processing plus proof | Erasure verification on request |
Use tracking and handling media systems to automate record-keeping and reduce human error in your audit trail. Annual vendor audits should verify that your destruction partner’s registrations remain current, their processes have not changed, and their security controls still meet your requirements.
A practical checklist IT pros rarely use — but should
Most data destruction guides stop at the technical steps. Here is where we diverge from that approach.
The biggest compliance failures we see are not technical. They happen because organizations treat hard drive destruction as a one-time cleanup rather than an ongoing program. Drives accumulate in storage closets for months. Vendors get renewed without re-auditing. Certificates of destruction get filed in a shared drive nobody can find during an audit.
The fix is a repeatable, signed-off checklist that runs every quarter. It should include confirmation that new assets were added to the inventory, that any drives held in staging have a scheduled destruction date, and that your vendor’s registrations are still current. Share this checklist with your compliance officer and your CFO. When upper management sees destruction as a scheduled, documented program rather than an IT task, budget and resources follow.
The equipment destruction perspective reinforces that proactive programs consistently outperform reactive ones in audit outcomes. Ad hoc destruction creates gaps. A repeatable process closes them before regulators ever ask.
Get compliant e-waste and data destruction solutions
If your organization is ready to move from ad hoc disposal to a fully compliant, documented destruction program, the right partner makes all the difference.

Recycle for Life provides compliant e-waste solutions that cover hard drive destruction, IT asset decommissioning, and environmentally responsible recycling under one roof. Our services include on-site destruction with witnessed certificates, computer recycling services for full device disposal, and a streamlined IT asset disposition process that handles inventory, destruction, and documentation for you. Get a free quote and let us handle the compliance complexity so your team can focus on what matters.
Frequently asked questions
How do I verify my hard drives were destroyed properly?
Verification involves physical inspection of particle size, review of destruction certificates, and third-party audits. Readback verification for Clear and Purge methods confirms data is inaccessible before media leaves your control.
Why is particle size important in hard drive destruction?
Particle size determines whether destroyed drives can be reassembled to recover data. HDDs require destruction to under 6mm and SSDs to under 2mm for the highest security assurance.
How often should vendors be audited for compliance?
Audit vendors at least annually to confirm their registrations remain current, their destruction processes have not changed, and their security controls still meet your regulatory requirements.