
Network equipment disposal is the process of securely decommissioning outdated network hardware to protect sensitive data and comply with environmental law. IT managers who treat this as a routine hardware swap rather than a structured security and compliance event expose their organizations to data breaches, regulatory fines, and environmental liability. Routers, switches, and fiber channel devices store configuration data, credentials, and network topology across multiple persistent memory locations.
What does a network equipment disposal guide cover?
A structured network equipment disposal guide addresses three parallel workstreams: data sanitization, environmental compliance, and value recovery. Most organizations focus only on the first and ignore the other two until an audit or a regulatory notice forces the issue. Getting all three right from the start is what separates a defensible disposal program from a liability.
The IT Asset Disposition (ITAD) industry uses this term to describe the full lifecycle process. ITAD is the recognized industry standard for what most IT managers informally call “equipment disposal.” Using ITAD terminology in vendor contracts and internal policies signals that your organization understands the regulatory and security stakes involved.
What preparatory steps should you take before disposal?
Preparation determines whether your disposal process is defensible or just documented. Before a single device leaves your rack, three tasks must be complete.
Build a complete asset inventory. Every device scheduled for disposal needs a record that includes make, model, serial number, data classification, and last known configuration state.
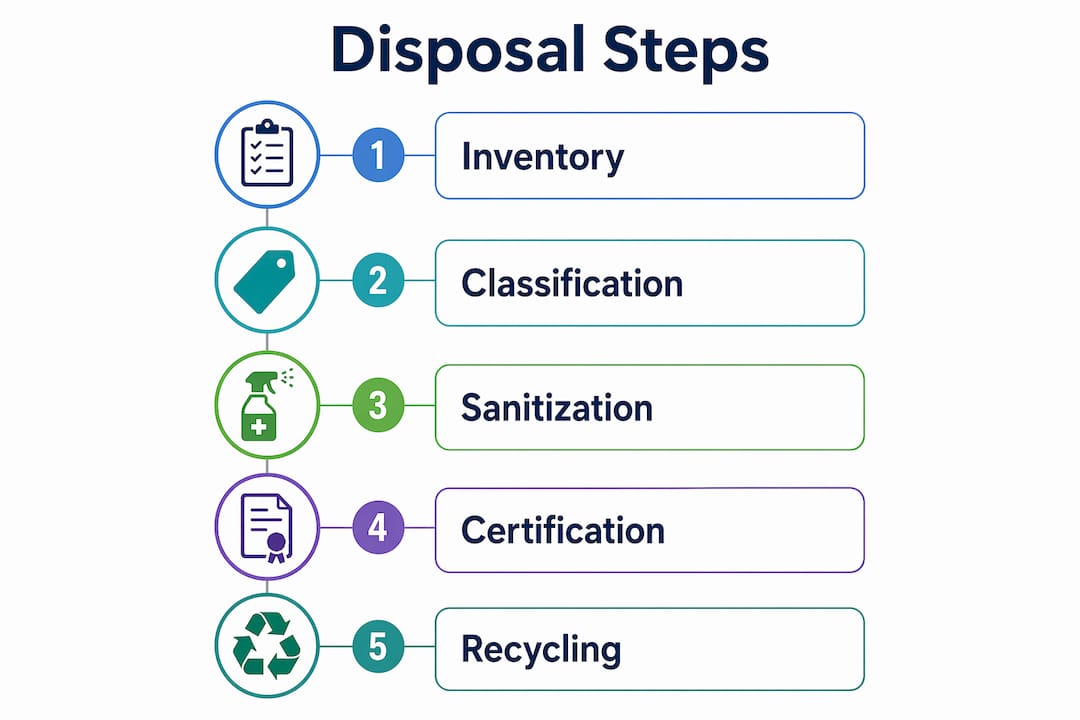
Classify data sensitivity by device type. A core switch that handled financial transaction traffic carries a different risk profile than an edge access point in a conference room. 2 defines media sanitization as the process of making data access infeasible, and it explicitly recommends matching sanitization techniques to the sensitivity of the data stored on each device. That match cannot happen without classification.
The table below maps common network hardware types to appropriate methods.
| Device type | Recommended method | Notes |
|---|---|---|
| Managed switches and routers | Purge via vendor decommission command | Clears all persistent stores |
| Fiber channel switches (Broadcom) | switchDecommission command | Requires authorization code |
| Unmanaged switches | Clear or Destroy | Limited software access |
| End-of-life hardware with no vendor support | Physical destruction | No defensible software path |
Pro Tip: Before scheduling any device for disposal, pull the vendor’s decommission documentation and confirm whether an authorization code or a support ticket is required. Broadcom’s process, for example, requires a node-specific token that must be requested in advance. Missing this step can delay your disposal timeline by days.
Consulting a network closet organization guide before disposal also helps you identify devices that were never formally inventoried, which is a more common problem than most IT teams admit.
How do you securely erase data from network hardware?
Factory resets do not constitute secure sanitization. This is the single most consequential misunderstanding in network hardware recycling. A factory reset typically restores operating system defaults but leaves configuration partitions, FRU (Field Replaceable Unit) data, SEEPROM, boot variables, and compact flash memory intact. Any of those stores can contain IP addresses, VLAN configurations, authentication credentials, and network topology data.
Broadcom’s Fabric OS switchDecommission command is the correct tool for fiber channel switches running Fabric OS. It clears compact flash memory, IP configurations, and FRU data in a single controlled execution. The command permanently disables the device after execution, which is why it requires a device-specific authorization code before it runs.
The secure sanitization process for managed network devices follows this sequence:
- Obtain the vendor-specific decommission authorization code or token from the manufacturer’s support portal.
- Confirm the device serial number matches the authorization code. Authorization codes are node-specific and time-limited, preventing unauthorized reuse.
- Execute the decommission command in a controlled maintenance window with a second technician present to witness and document the process.
- Capture the command output log and attach it to the device’s asset record as proof of sanitization.
- Physically label the device as sanitized and segregate it from active equipment immediately.
- If the device cannot be sanitized via software (no vendor support, hardware failure), proceed directly to physical destruction.
“Defensible sanitization requires documented, verified clearing of every persistent storage area on a device, not just the primary operating partition.” This principle, drawn from Broadcom’s Fabric OS decommission workflow, applies equally to Cisco IOS devices, Juniper Junos platforms, and any other managed network hardware.
This is not the same as breaking the chassis. A destroyed hard drive or flash module is unrecoverable. A cracked switch chassis with intact flash memory is not sanitized.
Pro Tip: Document the name, title, and employee ID of every person who executes or witnesses a decommission command. If your disposal process is ever audited, witness records are as important as the command output logs.
For a deeper look at what secure data destruction actually requires at the hardware level, Recycle for Life has published a detailed breakdown of the methods and their legal defensibility.
What environmental laws govern network hardware recycling?
Electronic waste management for network hardware is regulated at both the federal and state level in the United States. The EPA does not operate a single federal e-waste recycling law, but 25 US states plus Washington DC have enacted electronics recycling laws with varying scope, covered device categories, and compliance deadlines. Businesses operating across multiple states face a patchwork of obligations that cannot be addressed with a single policy.
Key regulatory and registration frameworks include:
- Extended Producer Responsibility (EPR): The ITU’s e-waste policy toolkit promotes EPR frameworks that place disposal obligations on manufacturers, which affects how your vendors are structured and what documentation they can provide.
For a state-by-state breakdown of electronics disposal regulations, Recycle for Life maintains a current reference that maps requirements by jurisdiction. This is the fastest way to confirm what your organization owes in each state where you operate.
How do you choose a qualified network equipment recycler?
The recycler you select inherits your compliance risk. A vendor that cannot provide written proof of destruction leaves a gap that regulators and auditors will notice. Choosing an unvetted vendor to save money on disposal costs is a false economy.
Evaluate recyclers against these criteria before signing any contract:
- Regulatory status: Confirm the vendor's EPA ID and state regulatory status directly with the agencies, not just from the vendor's marketing materials.
- Data destruction certificates: The vendor should provide a certificate of destruction recording the quantity, description, and method, with your serial list attached if you supply one.
- Value recovery transparency: If your equipment has resale value, the vendor should provide an itemized accounting of recovered value versus disposal costs.
- Insurance and liability coverage: Confirm the vendor carries adequate liability coverage for data breaches that occur during transit or processing.
The EPA’s model contract language gives procurement teams ready-to-use clauses that impose minimum registration requirements on recyclers. Paste these clauses directly into your vendor agreements rather than writing custom language from scratch.
A vendor who cannot produce clean samples quickly is telling you something important about their actual process.
Used network equipment with resale value should be assessed before disposal. Switches, routers, and fiber channel hardware from brands like Cisco, Juniper, and Arista often retain significant secondary market value. A qualified ITAD vendor will separate recoverable assets from true end-of-life equipment and apply the recovered value against your disposal costs. For guidance on sustainable asset recovery, Recycle for Life covers the full process from valuation to compliant disposition.
What are the most common disposal mistakes to avoid?
Even organizations with written disposal policies make predictable errors. The following mistakes account for the majority of compliance failures and data exposure incidents in network hardware disposal.
- Relying on factory resets as sanitization. As covered above, a factory reset leaves multiple data stores intact. This is the most common and most dangerous mistake in the process.
- Ignoring state-level recycling laws. Because electronics recycling laws vary by state, a policy built around one state’s requirements will be non-compliant in others. Multi-state operators need jurisdiction-specific review.
For a broader look at the hardware recycling challenges organizations face in 2026, Recycle for Life has documented the most common failure points and how to address them before they become audit findings.
Key takeaways
Secure network equipment disposal requires a structured program that addresses data sanitization, environmental compliance, and vendor accountability simultaneously, not as separate afterthoughts.
| Point | Details |
|---|---|
| Factory resets are insufficient | Use vendor-specific decommission commands to clear all persistent data stores on managed devices. |
| State laws vary significantly | Confirm jurisdiction-specific recycling requirements for every state where your organization operates. |
| Require compliant recyclers | Require an EPA ID and state regulatory standing in contracts and verify them with the agencies. |
Why disposal governance is the real IT security gap
We have reviewed disposal programs at organizations that had excellent patch management, strong access controls, and mature incident response plans. Almost every one of them had a weak or informal disposal process. The pattern is consistent: IT security investment follows perceived threat vectors, and decommissioned hardware feels like a solved problem the moment it leaves the building.
The uncomfortable reality is that a switch leaving your data center with intact SEEPROM data is a data breach waiting for a motivated buyer. Secondary market resellers are not all scrupulous, and network hardware with recoverable configuration data has real intelligence value to competitors and attackers alike.
What we have found actually works is treating disposal as a security control, not a logistics task. That means it belongs in your security governance framework alongside vulnerability management and access reviews. It means your disposal vendor is vetted with the same rigor as your cloud providers. And it means your sanitization records are stored with the same retention policy as your security incident logs.
The organizations that get this right are not spending more money. They are spending the same money more deliberately, with compliant vendors, documented processes, and quarterly reviews. The ones that get it wrong find out during an audit or, worse, after a breach.
Protect your organization with compliant disposal services
When your network refresh cycle produces a stack of decommissioned switches, routers, and fiber channel hardware, the disposal decision carries real security and compliance weight. Recycle for Life provides compliant e-waste recycling and data destruction services built for exactly this situation. Drives processed through Recycle for Life are physically destroyed and covered by a Certificate of Destruction.

For organizations with higher-value assets, Recycle for Life also offers IT asset recovery quotes that assess resale potential before disposal, so you recover value rather than simply paying to dispose. Whether your priority is data security, environmental compliance, or both, Recycle for Life delivers a process that holds up under audit.
FAQ
What is the difference between a factory reset and secure sanitization?
A factory reset restores default software settings but leaves configuration data, credentials, and network topology intact across multiple persistent storage areas including SEEPROM, FRU data, and compact flash. Secure sanitization uses vendor-specific decommission commands or physical destruction to clear every data store on the device.
Which registration should I require from a network equipment recycler?
Require an EPA-registered, state-regulated recycler that provides written proof of data destruction and recycling. Verify current registration status directly with the regulator before signing any vendor contract.
Do I need to follow different rules in different states?
Yes. Twenty-five US states plus Washington DC have enacted electronics recycling laws with different covered device categories, fees, and deadlines. Businesses operating across multiple states must review jurisdiction-specific requirements for each location where they generate e-waste.
Can I sell used network equipment instead of recycling it?
Yes, and you should assess resale value before committing to disposal. Managed switches, routers, and fiber channel hardware from major vendors often retain secondary market value. A qualified ITAD vendor will separate recoverable assets from true end-of-life equipment and apply recovered value against your disposal costs, but only after completing verified data sanitization.
How long should I retain disposal documentation?
These records are your primary defense in a regulatory audit or a post-disposal data breach investigation.