
Most organizations believe that handing off old computers and servers to a recycling vendor automatically protects their data. That assumption is wrong, and it has real consequences. Data breaches traced to improperly retired IT assets have cost businesses millions in regulatory fines and reputational damage. Secure equipment recycling is a fundamentally different process from basic e-waste drop-off. This guide walks you through what secure equipment recycling actually requires, how the workflow is structured, and how to choose a provider that protects your organization at every step.
Table of Contents
- Understanding secure equipment recycling
- Key steps and controls in secure recycling workflows
- Sanitization standards, validation, and when device reuse is safe
- Choosing the right provider: Registrations, records, and compliance
- Why secure equipment recycling isn’t just IT’s job: Organizational lessons
- How we support secure recycling for your business
- Frequently asked questions
Understanding secure equipment recycling
Strip away any one of those three elements and you no longer have a secure process. You have a liability.
Generic e-waste recycling focuses primarily on diverting electronics from landfills. That goal matters, but it says nothing about what happens to the data still stored on drives, flash memory, or embedded chips. Secure equipment recycling, by contrast, is governed by sanitization standards that are specifically designed to address data risk alongside environmental responsibility.
2, published by the National Institute of Standards and Technology. That standard applies regardless of whether the device is being reused, donated, or destroyed.
Here is a quick comparison of generic e-waste recycling versus secure equipment recycling:
| Feature | Generic e-waste recycling | Secure equipment recycling |
|---|---|---|
| Certificates of destruction | Rarely issued | Standard deliverable |
| Compliance support | None | Supports HIPAA, GDPR, SOX |
| Environmental controls | Basic | Compliant downstream recycling |
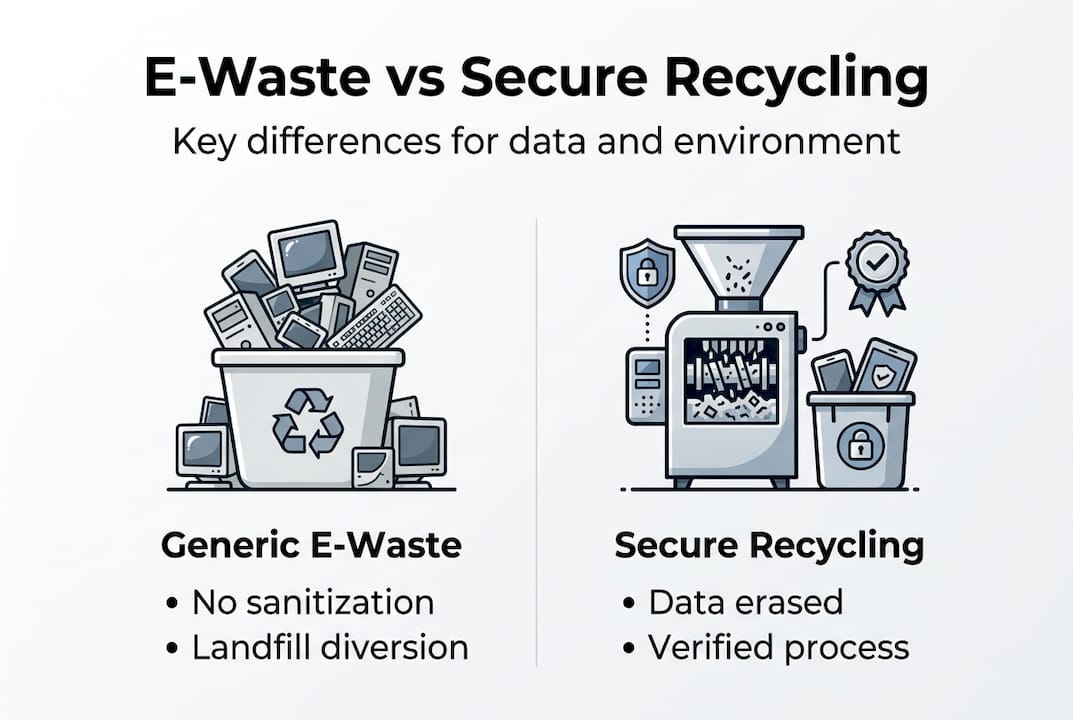
When reviewing old equipment disposal steps at your organization, the absence of a sanitization record for any retired device is a red flag.
Key characteristics that define a secure recycling program include:
- Asset-level tracking from collection through final disposal
- Downstream vendor accountability for environmentally responsible processing
- Certificates of data destruction delivered to the client as audit evidence
2 is the baseline for any program that claims to protect your organization.
Understanding this definition makes it easier to evaluate vendors, design internal policies, and respond confidently to auditors or regulators asking how your organization retires technology.
Key steps and controls in secure recycling workflows
Now that we’ve defined secure equipment recycling, let’s look at how these principles are applied in real-world business and IT workflows. The process follows five structured steps, and skipping even one creates gaps that auditors and regulators will find.
Here is how each step works in practice:
-
Asset inventory. Before any device leaves your building, every unit is cataloged. Serial numbers, device types, storage media, and assigned users are recorded. This creates the baseline your audit trail depends on.
-
Secure logistics. Equipment moves under controlled conditions. Sealed, tamper-evident containers and tracked transportation prevent unauthorized access between collection and processing. For high-sensitivity organizations, on-site processing eliminates transport risk entirely.
-
Data sanitization. The right method is applied to each device based on media type, classification level, and downstream intent. More on choosing the correct method appears in the next section.
-
Verification and validation. Every sanitized device is checked to confirm the process succeeded. Automated logs capture outcomes for each unit. This documentation becomes the evidence your compliance team needs.
-
Compliant downstream recycling. After data is addressed, materials are processed through a compliant recycler. This step ensures hazardous components like lead and mercury are handled properly and kept out of landfills.
The equipment destruction process and secure computer recycling both follow this five-step model when executed by a qualified ITAD provider.
Process documentation is what separates defensible compliance from wishful thinking. Aligning these records with your IT asset management practices makes the entire process sustainable across equipment refresh cycles.
Pro Tip: Request sample documentation from any recycling vendor before signing a contract. If they cannot show you a sample certificate of destruction and sanitization log within minutes, assume those records do not exist.
Sanitization standards, validation, and when device reuse is safe
Understanding the workflow, it’s crucial to choose the right sanitization method, and know when each is appropriate. 2 defines three primary approaches, and the correct choice depends on media type, data sensitivity, and whether the device will be reused.
Here is a comparison of the three main sanitization methods:
| Method | Best for | Reuse possible? | Validation method |
|---|---|---|---|
| Software wiping | HDDs, low-sensitivity data | Yes | Automated logs |
| Physical destruction | High-sensitivity, unrecoverable media | No | Certificate of destruction |
That validation piece is non-negotiable. A wipe that was interrupted, applied to the wrong drive, or performed by outdated software leaves recoverable data behind. Without a log confirming success, you cannot prove compliance.
When a self-encrypting drive has its encryption key deleted, the stored data becomes permanently inaccessible without physically destroying the device. This makes reuse practical for modern hardware while still meeting regulatory standards.
The decision between reuse and destruction involves several factors:
- Regulatory environment. Healthcare organizations under HIPAA often require destruction for certain media types regardless of sanitization.
- Drive condition. Damaged or failing drives should always be destroyed. Attempting to wipe a failing drive risks leaving recoverable data.
- Downstream destination. A device being resold internally faces different standards than one being donated externally.
Reviewing sanitization methods for devices before a major equipment refresh gives your IT team a clear decision framework before assets leave the building. For situations requiring physical destruction, the physical destruction option provides on-site destruction with documented outcomes.
Choosing the right provider: Registrations, records, and compliance
Selecting the best recycling method is only one part. The right provider ensures those standards are rigorously followed every time, not just on paper.
When evaluating vendors, ask these questions directly:
- What registrations does your facility hold, and are they current?
- What does your certificate of destruction include, and how quickly is it delivered?
- How are subcontractors or downstream vendors vetted?
Here is a quick-reference table mapping key registrations to their coverage areas:
| Registration | Data security controls | Environmental safeguards | Worker safety | Third-party audited |
|---|---|---|---|---|
| ISO 27001 | Yes | No | No | Yes |
Provider compliance does more than satisfy auditors. It shifts liability. When a compliant ITAD provider fails to sanitize a device and data leaks, your organization’s documented due diligence in selecting and managing that vendor provides critical legal protection. Without it, your organization absorbs the full regulatory risk.
For businesses seeking IT asset disposition services, the provider’s registrations should appear in the service agreement and be verifiable through the regulator’s public registry. Don’t accept verbal assurances. Require documentation.
For organizations with specialized hardware, secure recycling for batteries and other components requires providers with specific environmental registrations beyond standard ITAD scope.
Why secure equipment recycling isn’t just IT’s job: Organizational lessons
Here is something most IT-focused guides skip entirely: a significant portion of data exposure events tied to retired equipment trace back to decisions made outside the IT department. Finance teams authorizing equipment sales without flagging drives for sanitization. HR departments donating old laptops as a goodwill gesture. Facility managers clearing out server rooms during a lease transition without notifying IT.
These are not malicious acts. They are well-intentioned mistakes made by people who were never taught that a documented sanitization program is what separates compliance from exposure. Security and privacy compliance result from formal programs, not assumptions about what recycling vendors will handle automatically.
Treating secure equipment recycling as a company-wide responsibility, not just an IT checklist, changes the risk profile entirely. Procurement needs to know what happens to a device at end-of-life before they approve the purchase. Finance needs to understand that residual value recovery from old assets must go through a secure channel, not a quick auction. HR needs a clear policy before donating equipment to schools or nonprofits.
Building this culture is ultimately about defensibility. When a regulator asks how your organization manages data on retired assets, the right answer involves cross-departmental accountability, not just a vendor contract. Your ITAD program insights should reflect that breadth from day one.
How we support secure recycling for your business
If you’re ready to simplify and secure your equipment recycling, our expert team can help at every stage of the process.

At Recycle for Life, we manage the full lifecycle from scheduled pickup to physical destruction with a Certificate of Destruction. Our clients receive certificates of destruction and recycling for their records. Every step is designed to eliminate guesswork and give your compliance team the evidence they need. Whether you need to retire a single server or manage a full fleet refresh, our e-waste recycling solutions and equipment destruction services are built around your security and environmental obligations. Request a free quote today and find out how straightforward secure recycling can be.
Frequently asked questions
What registrations should a recycling provider have?
When choosing a recycler, confirm it is EPA-registered and regulated by the state (in California, the DTSC), with annual reporting on how waste is handled.