
Audit-ready e-waste documentation means proof that every retired asset was sanitized, tracked, and disposed of lawfully, backed by paperwork that can be traced from the device to its final destination. If an auditor calls tomorrow, the first thing to pull is your certificate of sanitization alongside a serial-number inventory. Everything else builds from those two documents.
TL;DR:
- Most audits look for certificates of sanitization or destruction alongside a detailed asset inventory that you maintain yourself.
- Audit-ready documentation records what was processed, the method, and the date, with serial numbers listed when you supply them.
- Using standardized forms and keeping records for several years, along with internal checks, can help organizations rapidly prepare for audits.
- A comprehensive sanitization policy should specify methods, verification procedures, staff roles, and maintain consistent records across all asset classes.
Table of Contents
- What auditors actually check when reviewing e-waste
- The standards that set the documentation bar
- Turning sanitization rules into a working policy
- A checklist you can run before the audit lands
- Proving custody from pickup to final disposition
- How to walk an auditor through your evidence
- How Recycle for Life delivers the exact artifacts auditors want
- A 90-day sprint that gets you audit-ready
- Request a sample certificate before your next pickup
- FAQ
- Sources
What auditors actually check when reviewing e-waste
Auditors are not looking for good intentions. When any of those links is missing, the audit turns into a finding rather than a formality.
The evidence they ask for tends to repeat across industries and regulators:
- Certificates of sanitization or destruction recording what was processed, the method and the date, with your serial list attached when you supply it.
- Asset inventories listing make, model, serial number, and disposition date.
- Downstream processor receipts confirming where the material ended up.
Gaps in any of these categories create real exposure. A missing certificate can read as unverified data destruction, which invites questions about breach risk. Documentation isn’t paperwork for its own sake. It’s the only thing standing between your organization and a regulatory finding.
The standards that set the documentation bar
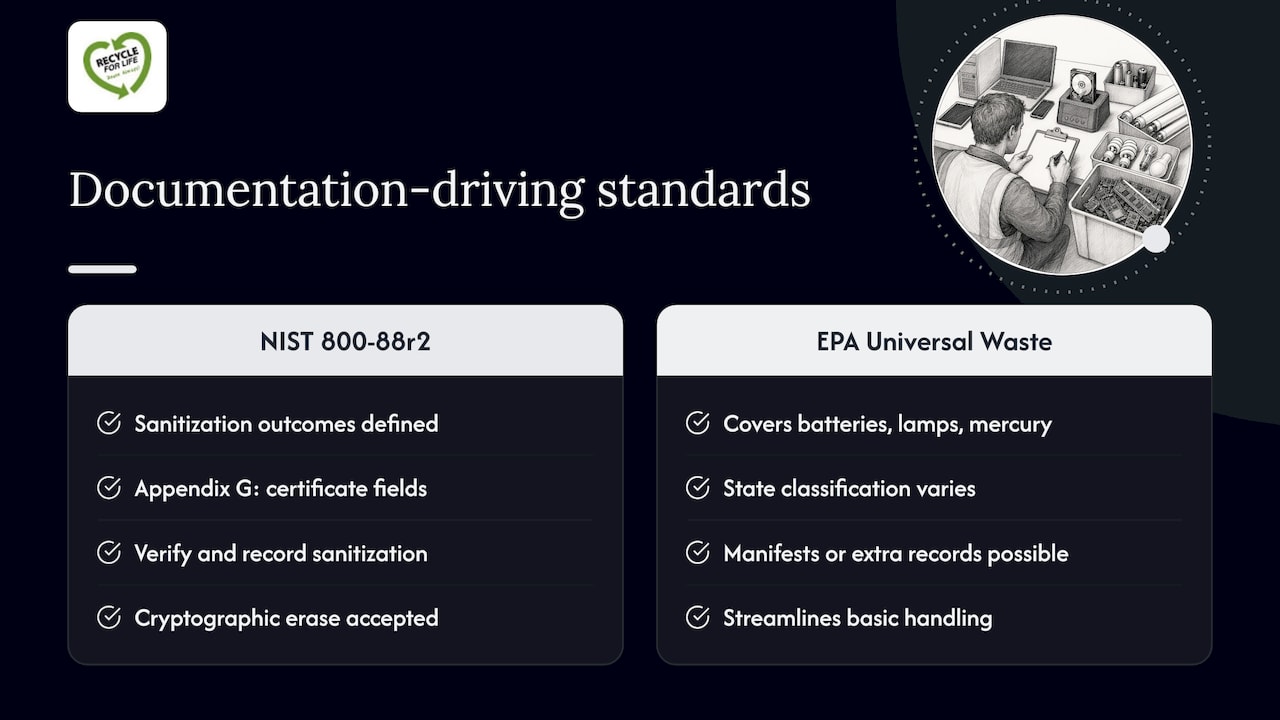
Most audit expectations trace back to a small set of federal guidance documents, even when a specific state or industry layers on extra rules.
The guidance also stresses that sanitization is not complete until it is verified and the verification is recorded.
On the hazardous-waste side, the EPA’s universal waste program streamlines handling requirements for batteries, lamps, mercury-containing equipment, pesticides, and aerosol cans.
That single clarification resolves one of the most common gaps auditors find in cloud-era IT asset disposition.
Practical triggers to watch: the volume of waste generated per month, whether your state treats electronics as universal waste or something stricter, and whether any retired devices held regulated data categories like health records or payment card information. Each of those answers shapes how much documentation a given disposal event needs.
Turning sanitization rules into a working policy
A sanitization policy only earns its name when it specifies method, verification, and accountability for every asset class you handle.
A policy that holds up under audit typically covers:
- Data classification tiers and which sanitization method (clear, purge, or destroy) applies to each.
- Roles and training requirements for staff or vendors performing sanitization.
- Equipment and tool versions approved for use, including calibration or validation schedules.
- Verification and validation procedures, including sampling rates for bulk sanitization runs.
For each individual asset, the record should capture manufacturer, model, serial number, asset tag, pre-sanitization data classification, method used, tool and version, verifying technician, date, and location.
Before relying on CE as a purge method, document the encryption scheme, confirm the keys are properly destroyed or rendered inaccessible, and review any cloud provider agreements for key management responsibilities. Without that documentation, CE looks like an assumption rather than a verified outcome.
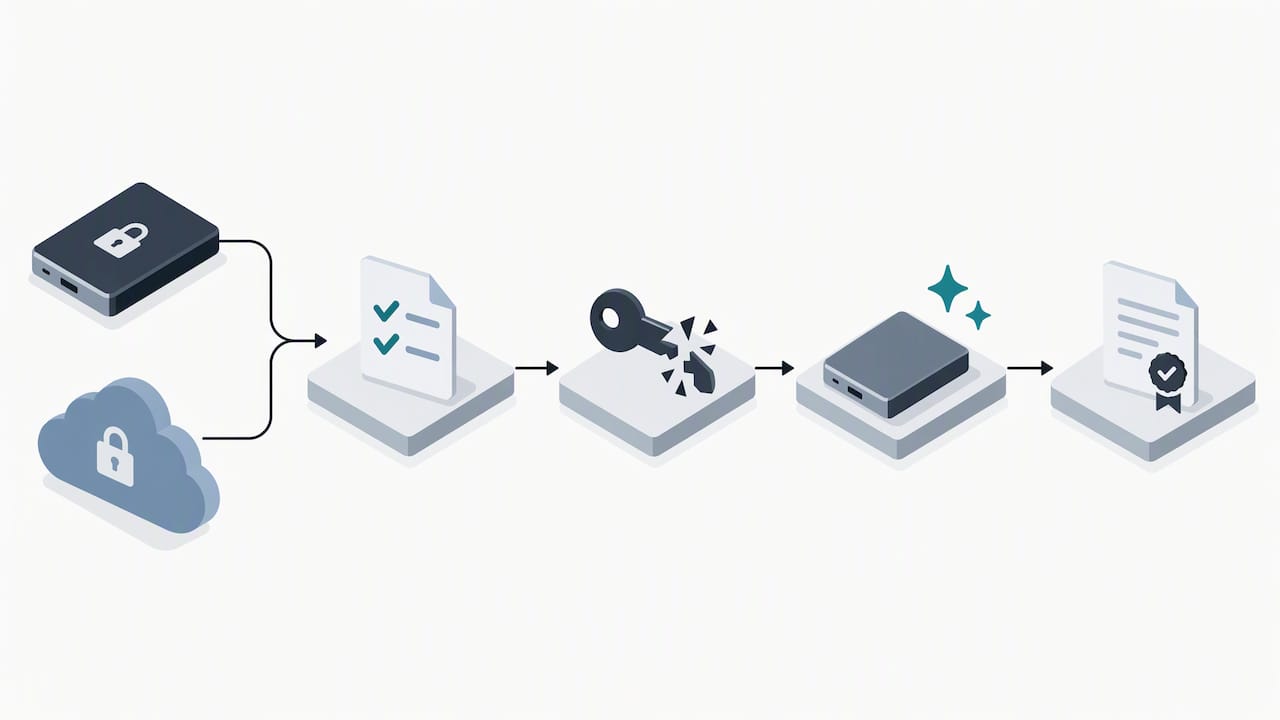
Verification and validation are not the same thing, and auditors know the difference. Verification confirms the sanitization method ran as intended on a given device. Validation confirms, often through sampling, that the overall process reliably produces sanitized output across a batch. Recording both, rather than just one, is what separates a defensible program from a checklist exercise.
Pro Tip: Keep a single verification log format across all vendors and internal technicians so an auditor can compare entries without translating between formats.
A checklist you can run before the audit lands
Start by pulling records in order of what an auditor asks for first, then work backward to fill gaps.
- Asset inventory with serials, because it anchors every other document to a specific device.
- Certificates of sanitization or destruction, because they are the direct proof data was destroyed.
- Downstream processor receipts, because they confirm final disposition rather than just pickup.
- Written policy and SOPs, because they show the process was designed, not improvised.
- Training logs, because they confirm the people doing the work were qualified to do it.
| Field | Purpose |
|---|---|
| Manufacturer and model | Identifies the exact device sanitized |
| Serial number or asset tag | Links the certificate to inventory records |
| Media type and classification | Shows what data sensitivity applied |
| Sanitization method | Records clear, purge, or destroy as used |
| Tool name and version | Lets an auditor verify the method was current |
| Verifying technician | Assigns accountability for the outcome |
| Date and location | Establishes the timeline for custody records |
On retention, it is generally recommended to keep most records for several years, with longer periods where legal or contractual obligations require it; following best practices in asset lifecycle management can help maintain accurate serial-level tracking and asset registers. Regular internal checks, such as quarterly reviews, help catch documentation gaps before an external audit occurs.
When a document is missing, don’t leave the gap silent. Log a corrective action: what was missing, when it was discovered, who closed it, and how. Auditors respond far better to a documented fix than to a surprise they find themselves.
Proving custody from pickup to final disposition
Every handoff needs its own record, not just a single receipt at the end.
An invoice confirms a commercial transaction took place. A certificate of destruction confirms the specific outcome: that sanitization or physical destruction actually happened to the listed items.
Downstream accountability closes the loop. The EPA’s resources on compliant electronics recyclers point generators toward collecting processor registrations or acceptance evidence as part of their own records, not just trusting that the hauler handled it correctly.
- Receipts that don’t describe what was collected make it hard to confirm what was processed. If you need to confirm specific assets, supply your serial list so it can be attached to the certificate.
- Unsigned or undated receipts raise the same question from a different angle: nobody can be held accountable for the handoff.
- Missing processor identifiers leave a generator unable to prove where the equipment actually ended up.
How to walk an auditor through your evidence
That sequence mirrors how the EPA’s compliance audit protocol frames evidence categories, and it keeps the conversation moving instead of backtracking.
- Build an indexed folder, physical or digital, that mirrors your checklist exactly.
- Attach a one-page cover sheet mapping each file to the question it likely answers.
- Pull a 30 to 60 item sample from your inventory in advance so you are not searching live.
- Confirm a witness or technician is available to answer verification questions directly.
Pro Tip: A short cover sheet that maps each document to its likely audit question often shortens the session more than the documents themselves.
When an auditor asks how you know a drive was actually wiped, point to the verification log entry, not just the certificate.
How Recycle for Life delivers the exact artifacts auditors want
Onsite data destruction maps directly to a signed certificate of destruction recording what was destroyed, the method and the date, with your serial list attached when you supply it before pickup. Recycle for Life’s onsite data destruction service and hard drive destruction service are built to produce those deliverables as a normal part of the process, not an afterthought. Ask for a sample certificate before scheduling a pickup so you can confirm the format matches what your audit actually requires.
A 90-day sprint that gets you audit-ready
Pull a 30 to 60 item inventory sample, validate sanitization on that subset, compile matching certificates, then schedule an internal audit. Add barcode scanning and digital certificate templates for low-effort, repeatable wins.
Request a sample certificate before your next pickup
Most compliance managers find out their documentation has gaps during the audit itself, which is the most expensive time to find out. Recycle for Life provides a Certificate of Recycling for pickups and a Certificate of Destruction for hard drive destruction, so you have paperwork to file.

A few places to start depending on what you need documented next:
- Onsite Data Destruction for certificate-backed, on-location sanitization.
- Hard Drive Destruction for witnessable destruction with documentation included.
- Recycling Services and IT asset recovery for pickup logs and reconciliation across larger asset lots.
Request a sample certificate to check the formatting against your audit requirements, then schedule a pickup when you’re ready.
FAQ
How do you ensure documentation is audit ready?
Run a quarterly internal check against your own checklist so gaps surface before an external auditor finds them.
How do you conduct a waste audit?
The EPA’s compliance audit protocol outlines the evidence categories inspectors typically check during this process.
What are the five Rs of e-waste management?
Definitions vary across organizations, but a common version covers reduce, reuse, repair, recycle, and recover, describing a hierarchy of preferred actions before equipment is disposed of entirely. The documentation practices in this guide apply once an asset moves past reuse and into recycling or destruction.
Where can you find official e-waste management rules?
Specific national e-waste rules vary by country and are not covered by the U.S. federal guidance referenced in this article. For U.S. organizations, the EPA’s universal waste guidance is the relevant starting point rather than rules from another jurisdiction.
What belongs in a certificate of sanitization?
A certificate should list what was processed, the method used, and the date, with serial numbers listed when you supply them.