
Most organizations assume that dropping off old computers at a community e-waste event is enough. It isn’t. Consumer recycling programs are built for convenience, not compliance. When a business disposes of servers, workstations, or mobile devices without following proper protocols, it exposes itself to data breach liability, regulatory penalties, and reputational damage that no drop-off bin can protect against. B2B electronics recycling is a completely different discipline, and understanding what separates it from consumer disposal is the first step toward protecting your organization.
Table of Contents
- What is B2B electronics recycling?
- Why compliant recyclers matter: Security, compliance, and trust
- The B2B electronics recycling process: Steps from pickup to proof
- Common mistakes and hidden risks in B2B electronics recycling
- The uncomfortable truth most organizations overlook
- Secure and sustainable electronics recycling solutions for your business
- Frequently asked questions
Key Takeaways
| Point | Details |
|---|---|
| Compliance is critical | B2B electronics recycling is driven by laws and standards for safe data destruction and documentation. |
| Document every step | Proper records like certificates of recycling and destruction are essential proof for audits and regulators. |
| Mistakes can be costly | Data mishandling or poor vendor choice can bring heavy penalties and reputational damage. |
| Ownership prevents problems | Making IT asset disposition an organizational priority avoids hidden risks and compliance gaps. |
What is B2B electronics recycling?
B2B electronics recycling refers to the structured, documented process by which businesses and organizations retire, sanitize, and responsibly dispose of end-of-life IT equipment. This is not a casual trip to the recycling center.
The types of equipment involved go far beyond old desktop computers. Organizations typically process:
- Servers and data center hardware with sensitive business and customer data
- Laptops, workstations, and tablets issued to employees
- Networking equipment such as routers, switches, and firewalls
- Mobile devices tied to corporate accounts and email systems
- Printers and multifunction devices that retain stored documents in onboard memory
- Peripherals and storage media including external hard drives, USB drives, and backup tapes
Each of these categories carries different data destruction requirements and different downstream material handling needs. A printer is not treated the same as a server rack. That specificity is exactly what distinguishes B2B from consumer recycling.
As the EPA notes, regulatory frameworks differ by jurisdiction, so B2B electronics recycling is best understood as a compliance-driven, evidence-producing process rather than a single uniform technical method. What a business in California must document differs from what a business in Texas must prove, and both operate differently from organizations subject to EU regulations.
The electronic waste recycling basics for businesses begin with understanding that every device your organization retires is a potential liability until it has been properly sanitized and recycled. Documentation, compliant vendors, and secure logistics are not add-ons. They are compliance-driven requirements that include secure logistics, data destruction, responsible recycling, and formal documentation.
Here is a quick comparison to clarify what separates B2B from consumer recycling:
| Factor | Consumer recycling | B2B electronics recycling |
|---|---|---|
| Data destruction | Usually not addressed | Required and documented |
| Compliance documentation | Not provided | Certificates issued |
| Equipment types | Personal devices | Enterprise hardware and storage media |
| Regulatory exposure | Minimal | High (HIPAA, FACTA, GDPR, SOX) |
The legal exposure column alone should reframe how your IT and operations teams think about end-of-life asset management.
Why compliant recyclers matter: Security, compliance, and trust
Not every recycler claiming to be “eco-friendly” or “compliant” has actually earned that designation through independent verification. In the B2B space, documentation is everything.
What do these registrations actually mean for your organization? A legitimate recycler is registered with regulators such as the EPA and, in California, the DTSC, which oversee it on an ongoing basis.
This matters because unregistered haulers answer to no regulator for how they handle your data or hazardous materials. They may wipe drives incompletely, sell equipment to overseas brokers, or fail to track where your data-bearing assets end up. The downstream risks are significant. For organizations in regulated industries like healthcare, finance, legal services, or government contracting, using an unvetted recycler is not just a mistake. It is a potential regulatory violation.
“The consequences of improper IT asset disposal are not hypothetical. They include regulatory investigations, civil penalties, and the kind of news coverage that takes years to recover from.”
When choosing a recycler, confirm it is EPA-registered and regulated by the state (in California, the DTSC), with annual reporting on how waste is handled.
| Standard | Focus area | Audit frequency | Data destruction requirement |
|---|---|---|---|
| No registration | Self-reported | None | No requirement |
When evaluating vendors, ask directly for their current registration documentation. Don’t accept verbal reassurances. A legitimate, compliant recycler will provide proof immediately.
Pro Tip: Ask your vendor for its EPA ID number and verify it independently with the EPA. Certificates can be faked, but registry entries cannot.
For organizations looking to go deeper on vendor selection, the process of secure electronics recycling involves more than just choosing the right label. Understanding how protecting data and the environment work together helps frame the right questions when evaluating a recycling partner.
The B2B electronics recycling process: Steps from pickup to proof
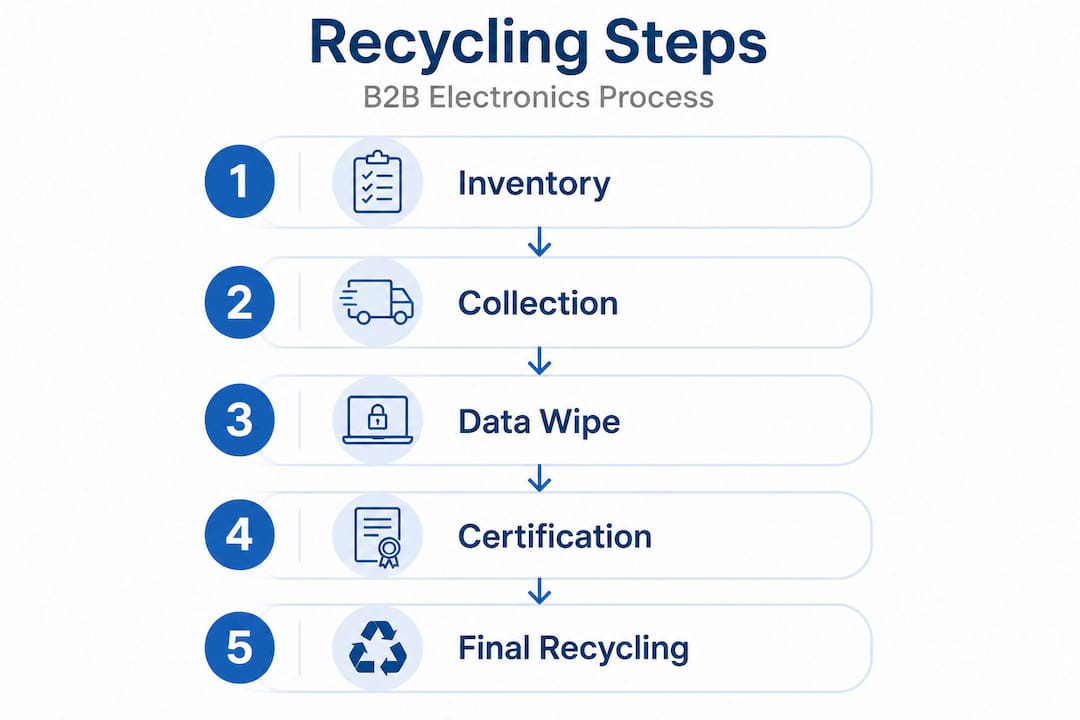
The standard B2B electronics recycling workflow is not a black box. When you work with a compliant vendor, you should be able to trace every device from your facility through data destruction and into final material processing. Here is what that process looks like in practice.
-
Inventory and scheduling. Your organization catalogs the assets to be retired, including serial numbers, device types, and storage media. The recycler confirms logistics and any special handling requirements before pickup.
-
Sorting and downstream processing. After data destruction is complete, devices are disassembled. Recoverable components (metals, plastics, circuitry) are sent to compliant downstream processors. Hazardous materials are handled according to environmental regulations. No untested material should go to landfill.
-
Certificate issuance. At the end of the process, you receive a Certificate of Recycling and, separately, a Certificate of Data Destruction for applicable devices. These documents record what was processed or destroyed, the method, and the date, with serial numbers listed when you supply your list before pickup. Keep them for your compliance records.
-
Audit support. If your organization is ever audited by a regulator or a client performing due diligence, these certificates are your evidence of compliance. Without them, you have no way to prove what happened to retired devices.
The proper e-waste recycling steps that a compliant vendor follows are tightly connected to your ability to demonstrate compliance. Reviewing a documented data destruction guide before you engage a vendor helps you ask smarter questions and set clear expectations up front.
Pro Tip: Before signing any vendor agreement, request a sample of their Certificate of Data Destruction. Review whether it includes the quantity, description, destruction method, and date, and whether your serial list can be attached.
There are also essential data destruction facts that every IT manager and compliance officer should understand before selecting a destruction method. Not all methods are appropriate for all media types, and choosing the wrong one can leave recoverable data on devices you believe were properly sanitized.
Common mistakes and hidden risks in B2B electronics recycling
Even organizations with solid IT policies make preventable mistakes in the end-of-life asset stage. These errors range from logistical oversights to serious compliance gaps that only become visible when something goes wrong.
Skipping data destruction before pickup. Some businesses believe that factory-resetting a phone or deleting files from a hard drive before handing equipment to a recycler is sufficient. It is not. Deleted files remain recoverable until overwritten multiple times or physically destroyed. Factory resets on mobile devices often leave partitioned data intact.
Accepting vague or incomplete documentation. A certificate that says “recycled on [date]” with no description of what was processed is weak documentation. It is a piece of paper. Regulations like HIPAA and FACTA require you to demonstrate how data was destroyed, not just that devices were sent somewhere.
Using vendors without an EPA ID number or state oversight. Unvetted recycling increases data security and environmental risks, which is precisely why regulators recommend working only with compliant vendors. The savings from using an unvetted vendor rarely offset the cost of a single compliance incident.
Treating all devices as equal. A laptop containing years of financial records requires a different destruction protocol than a conference room phone. Treating your entire retired IT fleet as a single category creates gaps where high-sensitivity devices slip through without proper handling.
“The most expensive compliance failure is the one you didn’t see coming because you assumed the process was someone else’s responsibility.”
Ignoring state-level regulations. Federal frameworks like HIPAA and FACTA are widely known, but many states have their own data disposal and e-waste laws with separate requirements. California’s SB 1386, for example, has specific breach notification requirements that can apply even when federal law might not trigger.
Understanding how to protect data during e-waste disposal starts with recognizing that every device is a potential exposure point, not just the obvious ones. A thorough review of compliance and eco-safe disposal practices can help your team build a more airtight process before the next refresh cycle.
The uncomfortable truth most organizations overlook
After working with organizations across industries, the pattern is consistent. The most dangerous e-waste failures do not happen because companies don’t know the rules. They happen because compliance gets treated as someone else’s problem.
IT teams assume Legal is tracking registration requirements. Legal assumes IT is vetting vendors. Procurement signs contracts based on price without checking registration status. Meanwhile, hundreds of data-bearing devices sit in a storage room waiting for someone to schedule a pickup.
The temptation to cut costs on IT asset disposition is real and understandable. Budget pressures are constant, and e-waste recycling feels like a back-office function with no clear return on investment. But this is exactly the kind of thinking that creates liability. The cost of a single data breach or regulatory fine dwarfs the difference between a compliant and unvetted recycler.
What actually works is assigning a named owner for the IT asset disposition process. One person or team accountable for vendor registration, documentation collection, and audit readiness. Without that accountability, the process gets fragmented and critical steps fall through.
The industry is also shifting. Clients increasingly ask for data destruction certificates before renewing vendor contracts. Insurance companies are starting to ask for recycling compliance documentation during cybersecurity policy renewals. Investors and ESG-focused auditors want proof that technology disposal aligns with sustainability commitments. Eco-friendly disposal solutions are no longer just about environmental goodwill. They are becoming table stakes for maintaining business relationships.
The organizations that get ahead of this shift are the ones that treat electronics recycling not as a logistics problem to solve cheaply, but as a compliance function to manage carefully.
Secure and sustainable electronics recycling solutions for your business
Taking control of your IT asset disposition process does not require building an internal program from scratch. The right partner handles the complexity while you retain the documentation and confidence you need for compliance.

Recycle for Life provides business e-waste services for organizations that need data destruction with a Certificate of Destruction and responsible recycling under one roof. Whether you are refreshing a single office or retiring a full data center, our process is built around your compliance requirements. Request an IT asset recovery quote today to see how we can recover value from your retired equipment while protecting your data and meeting regulatory standards. For organizations building a longer-term strategy, explore how our approach helps drive business sustainability alongside secure, compliant disposal.
Frequently asked questions
What types of electronics are included in B2B recycling?
B2B recycling covers computers, servers, mobile devices, networking equipment, and other data-bearing assets used in business settings. Typical workflows for these assets include secure logistics, data sanitization or destruction, downstream responsible recycling, and complete documentation and audit trails.
Why should businesses use compliant electronics recyclers?
Registration is verified by state and federal regulators, not self-reporting, making it a reliable indicator of genuine compliance capability.
What documentation should you receive after electronics recycling?
You should receive a Certificate of Recycling and a Certificate of Data Destruction that describes what was destroyed and how; serial numbers are listed when you supply them. Compliant recycling documentation serves as your formal compliance record for regulatory audits and client due diligence requests.
Are there different regulations for B2B recycling in the US versus Europe?
Yes, requirements differ significantly between regions.
What happens if data isn’t properly destroyed?
Data leaks from improperly retired equipment can trigger regulatory fines, business disruption, and lasting reputational damage. EPA-recognized programs specifically include requirements for safe management and destruction of data on used electronics, precisely because the consequences of failure are so severe.