
HIPAA-compliant recycling is defined as the secure disposal or sanitization of electronic devices containing protected health information (ePHI), ensuring that data is rendered completely unrecoverable before any device leaves your organization’s control. The HIPAA Security Rule, 45 CFR § 164.310(d)(2), mandates this for every device that has ever stored, accessed, or transmitted ePHI. That scope is broader than most organizations expect. Laptops, tablets, smartphones, servers, and even specialized medical equipment all fall under these rules. Getting this wrong exposes your organization to federal penalties, reputational damage, and patient harm.
What is HIPAA compliant recycling and which devices does it cover?
HIPAA-compliant recycling applies to every electronic device that has ever created, received, maintained, or accessed ePHI. That definition is intentionally wide. The devices covered include laptops, tablets, servers, mobile phones, and smartwatches, but the obligation does not stop at standard IT hardware.
Healthcare organizations frequently overlook a critical category: specialized medical technology. Imaging machines, patient monitors, infusion pumps, and connected wearables all store ePHI. Misclassifying these as ordinary IT hardware is one of the most common compliance gaps auditors find. Any device with a memory chip or storage component that touched patient data is in scope.
The full list of device categories subject to HIPAA recycling obligations includes:
- Workstations and laptops used by clinical or administrative staff
- Mobile devices including smartphones, tablets, and pagers
- Servers and network storage that hosted electronic health records
- Removable media such as USB drives, CDs, DVDs, and backup tapes
- Specialized medical equipment including imaging systems, diagnostic devices, and patient monitors
- Connected wearables and IoT devices that collected or transmitted patient data
Extending your compliance program to all of these device types is not optional. Failing to cover non-IT hardware leaves your organization exposed to the same penalties as any other HIPAA violation. A decommissioned MRI machine with an unwiped internal drive is just as dangerous as a discarded laptop.
What sanitization methods meet HIPAA standards?
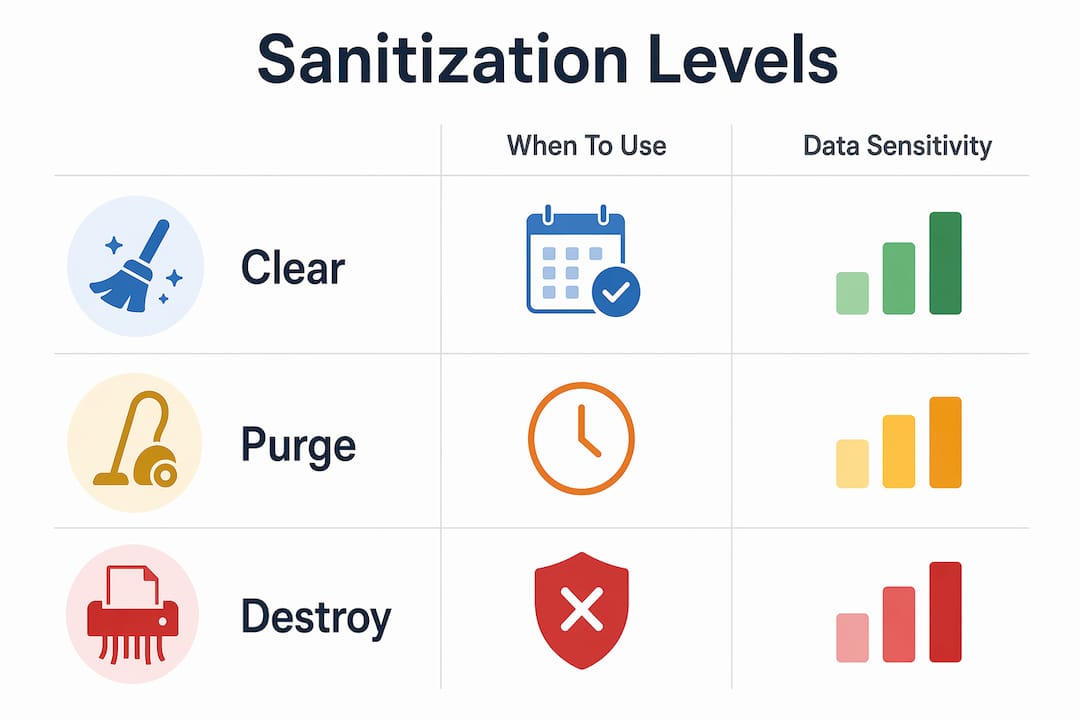
Each level is appropriate for different situations, and choosing the wrong one creates audit risk.
| Sanitization level | Method | When to use |
|---|---|---|
| Clear | Overwriting data with new values | Devices being reused internally with low data sensitivity |
| Destroy | Physical destruction or pulverization | Failed media, high-risk devices, or when sanitization cannot be verified |
The Destroy level is the most defensible option when device history is unclear. Physical destruction is recommended for failed drives or any media where software sanitization cannot be fully verified. Destruction provides a clear, auditable endpoint that leaves no ambiguity about data recovery.
A common misconception is that physical damage alone satisfies this requirement. Physical destruction must follow specific size and method standards to be defensible in an audit.
HIPAA does not mandate physical destruction for every device. Software-based overwriting at the Clear level satisfies the requirement for devices being reused within your organization, provided the process is documented and verified. Physical destruction becomes necessary when media has failed or when complete sanitization verification is not possible.
Pro Tip: Apply a risk-based approach. Select Clear, Purge, or Destroy based on data sensitivity, device condition, and whether the device will be reused or recycled externally. Document your rationale for each decision.
How to keep records and prove compliance
Documentation is the backbone of HIPAA recycling compliance. Detailed audit-ready records often matter more to HIPAA auditors than the destruction method itself. The principle is straightforward: if it is not documented, it did not happen.
A compliant documentation process covers every step from decommissioning to final disposal. Here is the required sequence:
- Create a serialized device inventory. Record the make, model, serial number, and data classification of every device before decommissioning begins.
- Execute a Business Associate Agreement (BAA). Any vendor that handles ePHI-containing devices during transport or destruction must sign a BAA. BAA agreements are required to establish vendor accountability and legal compliance throughout the process.
- Obtain a Certificate of Destruction. This document confirms the method used, the date, and the specific devices destroyed. It is your primary evidence in an audit.
- Retain records for six years. HIPAA requires organizations to keep documentation for a minimum of six years from the date of creation or the date it was last in effect.
Organizations must have formal policies addressing the final disposition of ePHI and related hardware, per 45 CFR § 164.310(d)(2)(i). Those policies must include procedures for disposal, reuse, and sanitization. A policy that exists only on paper and is never enforced provides no protection.
Pro Tip: Build your Certificate of Destruction file as a running log, not a one-time document. Auditors want to see a consistent, repeatable process across all device disposals, not a single record produced in response to an inquiry.
For a detailed look at building this documentation trail, the IT disposal documentation guide from Recycle for Life covers the full 2026 compliance process.
Best practices for building a HIPAA recycling program
A compliant recycling program requires policy, people, and vendor management working together. Neither element works without the other.
Policy and governance:
- Write internal policies that align with HIPAA Security Rule requirements and specify which sanitization level applies to each device category.
- Review and update policies at least annually or whenever new device types enter your environment.
- Assign a named compliance owner responsible for device decommissioning decisions.
Staff training:
- Include decommissioning protocols in onboarding for IT and clinical operations teams.
Vendor selection:
- Require all recycling and destruction vendors to sign a BAA before any device transfer occurs.
- Look for vendors with an EPA ID number and state regulatory standing. These registrations indicate responsible practices but must be verified within the context of the vendor's actual process.
- Confirm that the vendor issues Certificates of Destruction for every batch and can describe their sanitization method in writing.
- Understand that there is no official “HIPAA registration” for recycling vendors. Any vendor claiming to be “HIPAA compliant” is using a marketing term. What counts in an audit is a signed BAA, a documented process, and a Certificate of Destruction.
Device reuse vs. destruction:
- Reuse is appropriate only after rigorous, verified sanitization. If device history or data sensitivity is unclear, physical destruction is the safest and most defensible choice.
- Reuse reduces environmental impact and can recover asset value. Pair it with HIPAA compliance by using verified sanitization and documenting every step.
- For guidance on balancing compliance with environmental goals, the eco-friendly IT asset recovery resource from Recycle for Life outlines practical approaches.
Understanding how to stay HIPAA compliant in healthcare settings extends beyond device disposal and touches every operational process that involves patient data.
Key Takeaways
| Point | Details |
|---|---|
| Scope is wider than IT hardware | Medical devices, wearables, and imaging equipment containing ePHI are all subject to HIPAA recycling rules. |
| BAAs are non-negotiable | Every vendor handling ePHI-containing devices must sign a Business Associate Agreement before any transfer. |
| “HIPAA compliant” vendors do not exist | Verified processes, signed BAAs, and destruction certificates matter. Marketing claims do not. |
The compliance gap nobody talks about
The organizations we see struggle most with HIPAA recycling are not the ones ignoring it entirely. They are the ones who think they have it covered because they hired a vendor with a logo on their website.
The real problem is that most healthcare organizations treat device disposal as an IT task rather than a compliance function. That means the people making vendor decisions often do not know what a BAA is, have never asked to see a Certificate of Destruction, and assume that “HIPAA compliant” means something legally enforceable. It does not. There is no federal registration for recycling vendors. That phrase is pure marketing.
The second gap we see consistently is scope blindness. Organizations build a solid process for laptops and servers, then completely overlook the imaging machine being traded in, the infusion pump going to surplus, or the tablet used at the nursing station. Every one of those devices may hold ePHI. Every one of them needs the same documentation trail as a decommissioned server.
Our practical advice: treat your recycling vendor like any other business associate. Audit them. Ask for their process in writing. And build your Certificate of Destruction file as a living record, not a document you scramble to produce when an auditor calls.
Compliance and sustainability are not competing goals here. A device that is properly sanitized can be reused, which reduces e-waste and recovers asset value. The organizations that get this right are the ones that treat secure recycling as a process, not a one-time event.
How Recycle for Life supports compliant electronic waste disposal
Healthcare organizations and businesses that need a verified path to HIPAA-compliant device disposal can work with Recycle for Life for secure electronic waste recycling and documented data destruction services.

Recycle for Life provides on-site destruction and Certificates of Destruction for healthcare organizations. Every engagement includes a Certificate of Destruction for the drives we destroy. For organizations that need to understand what secure data destruction involves before committing to a program, Recycle for Life offers detailed guidance and free quotes. The service covers computers, servers, mobile devices, and specialized equipment, making it a practical option for healthcare organizations managing a wide device inventory.
FAQ
What is HIPAA compliant recycling?
HIPAA-compliant recycling is the secure disposal or sanitization of electronic devices that contain ePHI, ensuring data is rendered unreadable and irretrievable before the device leaves your organization’s control. It must comply with HIPAA Security Rule 45 CFR § 164.310(d)(2).
Does HIPAA require physical destruction of all devices?
HIPAA does not require physical destruction for every device.
What is a Certificate of Destruction and why does it matter?
A Certificate of Destruction is a formal document confirming the method, date, and specific devices destroyed by a vendor. It serves as your primary audit evidence and must be retained for at least six years under HIPAA documentation requirements.
Do recycling vendors need to sign a Business Associate Agreement?
Yes. Any vendor that handles ePHI-containing devices during transport, sanitization, or destruction must sign a BAA. Without a signed BAA, your organization retains full liability for any data breach that occurs during the vendor’s handling of those devices.
What does “HIPAA compliant recycling vendor” actually mean?
It means nothing legally enforceable. No federal body issues HIPAA registration for recycling vendors.
Industries we serve
- Hospital e-waste recycling
- Electronics recycling for law firms
- Electronics recycling for accounting firms
- Electronics recycling for dental offices
- Electronics recycling for property managers
- Electronics recycling for hotels
- Electronics recycling for warehouses